Task Bar Hero has disclosed a data breach that exposed player identifiers, IP addresses, and device information. Publisher Nugem Studio says an attacker downloaded records from its external game-server service, and warns that the information could be used in scams impersonating the development team.
The official notice, signed November 12, identifies affected accounts as those that played the game before November 9 at 3:59 p.m. KST (6:59 a.m. UTC).
What Was Exposed
According to the studio, an attacker exploited a vulnerability in the management tool of its external game-server service and downloaded player information from October 17 through November 8. The provider notified Nugem of the incident on November 9, KST.
The exposed records include:
- Steam profile IDs, also known as SteamID64.
- Game-server account IDs and registration dates and times.
- Last-login dates and times, along with the IP address used.
- Motherboard model names or computer names.
- Operating-system types and versions.
- Whether an account had been restricted or deleted.
The studio says the exposed information cannot by itself let someone log in to Steam, make payments, or access or alter other players’ game data. Its warning concerns the possibility of scams using the exposed information to impersonate the development team. A message can look convincing when the sender knows which game you play; asking you to “verify” your account through their link is where that familiarity becomes dangerous.
The Studio Says Access Has Been Blocked
Nugem says the provider fixed the vulnerability and blocked the attacker’s access. Both companies reviewed server-data permissions and security settings, while the developer also strengthened the security of accounts with access to those servers. The provider has reported the incident to South Korea’s Personal Information Protection Commission and Korea Internet & Security Agency, according to the notice.
At the time of the announcement, the studio said it had received no confirmed reports of misuse. It has not given an affected-account count.
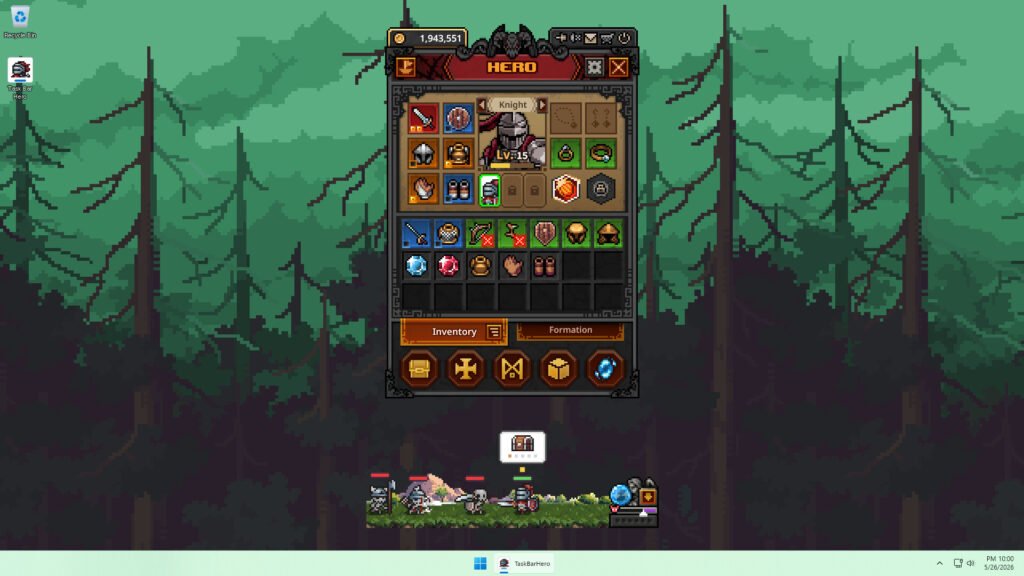
For a game designed to sit quietly along your taskbar, this is an unwelcome interruption. The idle RPG automatically battles enemies while you use your computer, and its items can be traded through the Steam Market. That makes the warning about unsolicited trade offers particularly relevant to its players.
Nugem says its team will never contact players first through Steam friend requests, chat, or trade offers. It recommends keeping Steam Guard Mobile Authenticator enabled and avoiding login or verification links received in messages. If someone approaches you about this breach, take the conversation directly to Nugem Studio’s support site instead of following their link.
Image: Nugem Studio / Tesseract Studio, via the official Steam store.